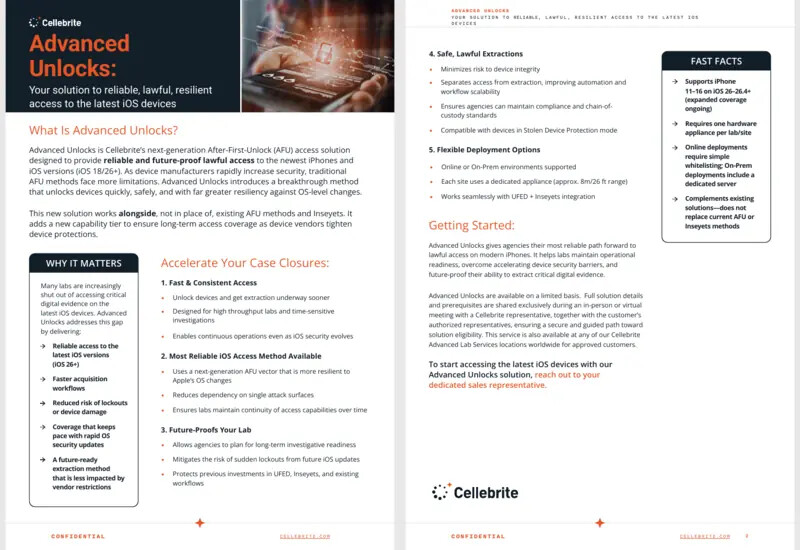
I was sent this article showing what appears to be a document by Cellebrite that was marked as confidential describing a recent Advanced Unlocks capability. The document is a few months old. This capability allegedly uses a dedicated appliance with a stated range of about 8 metres. Given the range they suspect it is to do with Bluetooth.
There is no mention of iPhones with MIE (hardware memory tagging, iPhone 17, Air and later) and it is not on the latest iOS version, which could suggest a patch.
Take a look at the article for yourself:
It would make sense that Cellebrite would choose to have capabilities like this one under development. When devices increase their security against physical attacks, the exploit developers will move towards a path of least resistance to exploit other components or circumvent the security measures that prevent the extraction, as we see with their automatic reboot cancelling exploits for iPhones. Since forensics labs contain devices in isolation to prevent network access and remote wiping, it is possible to make simulated / dummy network environments inside those containers where advanced labs can attempt exploit delivery without the risks.
The full document is available on request so it needs to be looked at further. While I do not intend to make discussion threads on this site regularly I think this is in a public interest.