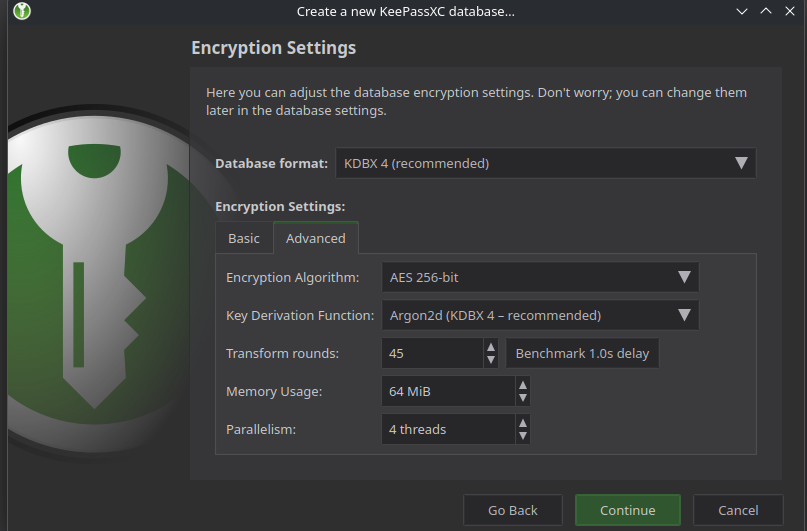
So how long would it take for a nation-state level adversary to brute force a 6 word diceware passphrase, with an offline copy of the file, assuming Argon2id
Your question doesn’t provide enough information to be answered.
This is zero information. Argon2id has parameters which change the work required to calculate a hash. To start you need to specify your parameters, at minimum.
You’re also just completely missing the point. Regardless of the parameters, if you would use the same ones for your 10 word and 6 word passphrase, your 10 word passphrase is literally 2^52.7 times safer than the 6 word passphrase.
2^52.7 is quite a large number to be rounding down to 1.
My point in explaining that your question is bad was not to get you to define a set of parameters, it was to point out that you don’t really understand these concepts as well as you think you do and probably shouldn’t make statements like “a 6 word passphrase is effectively just as safe as 10 words” so authoritatively.
I think you’re completely missing the point. It doesn’t matter if it’s a lot more. I don’t care it my password takes 1 billion years to crack or 9999 billion years to crack. Practically speaking it’s exactly the same.
Did you calculate how long it would take? I’d wager it’s an acceptable amount of time.
Someone who is completely missing the point certainly would think that about someone more knowledgeable than them trying to explain why they are mistaken, yes.
The point is that, for a six word passphrase, it’s only something absurd like 1 billion years to certain attackers. Given an adversary determined enough, they will do it much faster. Ten words guarantees via the laws of physics that your passphrase is between you and your god. Six words protects you only with your adversary’s lack of will.
These are not the same.
Acceptable to who? See, that’s kind of the entire point here. You cannot possibly claim objectively that one is as acceptable as the other when they are actually unfathomably distant in the purest terms.
The fact that you think there is just some formula to tell you how long it would objectively take demonstrates your lack of ability to speak as an authority in this subject.
Okay right so instead of thinking what may or may not be acceptable for some people, let’s just get an actual number to go off?
You’re saying 10 is fine but 6 is not. To me that’s actually quite authoritative. I think both are fine, but there’s a balance to strike when the passphrase needs to be remembered. Using your logic, this could go on indefinitely, someone who is more knowledgeable than you could come by and say 10 is not good, it’s got to be 20. And so on and so fourth.
So why not calculate the number, then we can have a hard metric to go off and decide if it’s reasonable, and for what threat model. I think against brute force and dictionary attacks, it suits all threat models. But let’s see.
Let’s assume:
- keepassxc defaults
- random 6 words
- 7776 wordlist
- NSA level adversary
I’d try and calculate it, but I think you should because, in your own words, you are much more knowledgeable than me.
Read my entire post maybe?
I literally did not. I said in no world is 10 the same as 6. Even if 6 suits your threat model that does not magically make it just as safe as 10. Obviously.
Someone more knowledgable than me wouldn’t say that because that’s absurd on it’s face.
Because it’s incalculable. I literally already said this. There are too many unknown variables.
What further variables do you need?
People calculate how long it takes to crack passwords of certain parameters all the time.
So is it incalculable, or is it guaranteed on the laws of physics? Which is it?
I have explained my position thoroughly. You are either not reading what I wrote or having difficulty comprehending. Regardless, I suggest reviewing my previous responses to find the answers to your questions and will not continue to repeat myself
You haven’t done that at all. You’ve just said I’m right you’re wrong.
You have said we can’t know if 6 words is secure because there are missing variables. I have then outlined every variable required to answer the question and you have evaded it entirely. All you’ve done is said you know more than me and trust me bro.
You’ve said 10 words is secure, guaranteed by the laws of physics (ie. calculable mathematically) but it’s impossible to calculate if 6 words is secure. It’s not that hard, it’s literally how many guesses per second can be made divided by the possible combinations of the passphrase.
You’ve not laid out a position of any substance whatsoever.
To further highlight your inconsistencies, you’ve said previously in another post that 5-8 words of a diceware passphrase is strong enough.
So you’ve not actually done anything, in terms of disproving what I have said, or proving what are you saying. Get back to me when you’ve done the maths.
If you think me saying that 5-8 words is strong enough for most use cases is even remotely inconsistent with the points I’ve made in this thread I suggest you spend less time weirdly harassing someone on a forum by scrolling through their post history to reply to it after you got mad they disagreed with you in another thread and more time actually reading the posts you’re getting mad at. You literally just don’t even know what’s being discussed. Because of the strange nature of your actions here, I am now blocking you, so you will not hear from me further.
How many bits would you view as the requirement for a password manager if you assume the adversary gets possesion of the database file?
Thanks, can it generate the shares in a form other then QR codes? I dont have a printer at the moment
You don’t need a printer, just click the download button, you’ll have the QR code and also an alphanumeric code.

That happens if you’re opening the website with Mullvad browser (and probably some other hardened browsers). Some privacy settings mess with it.
Retry with another browser or relax some settings.
Is there a download button for the page?
Please read the infos at the bottom of the page.
Q&A
What if 2of3.ente.com is unavailable?
A fully offline HTML recovery page is included when you use “Download all cards”. Open that file locally, add any two matching cards, and recover without needing the site. 2of3 is also open source, so the format is inspectable and recovery is not locked to one hosted service.