A document by Netzpolitik reveals that German police are sneakily abusing the linked devices feature in messengers to access the messages of suspects using encrypted messengers like Signal without needing to crack the encryption.
Are there any settings in Molly or Signal that can prevent this attack? This seems almost too easy for them. Does ‘Registration Lock’ PIN prevent this? (Assuming they don’t have your PIN.)
I also wish it didn’t take so many clicks to get into someone’s profile and view how many devices they have linked. It would be cool if that was displayed more prominently.
I don’t have an answer (someone with another device/PC at hand needs to test this), but this document is more like a general procedure rather than directly connected to any service.
On the Signal side, only a phishing account disguised as “Signal Support” asked for the SMS code, which allowed the connection, if I understood correctly. The German Federal Office for Information Security (BSI) suspects this phishing account to be of foreign state-level origin.
As far as I can see, Signal is only ever mentioned as an example for a messenger. Could you check the headline, @fria ? If I understand correctly, these show two different instances. (I’m sorry, if I misunderstood the material.)
Anyway, what still applies here is who they are targeting. It is unlawful for police in the EU to deploy such a means targeting a person without legitimate reason and connection/association.
I could see a SIM swapping attack (back and forth) feasible for them, though.
Then again like I said, I don’t know how Signal handles authorization of linked devices and someone needs to provide that info.
They use this attack against several messengers, not just Signal, yes. Signal does get mentioned by name. I changed the title to reflect that now.
The example of Signal phishing was a foreign state actor likely, it just shows a good example of how easy it can be to log in to someone else’s account when the only security is SMS verification.
I don’t really trust these types of safeguards. At the end of the day the government will use whatever they want against whoever they want.
No, as the attack relies on the user making a mistake & giving out the necessary data to the attacker for the attack to proceed. Once again, it’s the user who is the weakest link in the chain of security. The way to defend against this is to not send your 2FA codes anywhere, not to scan any suspicious QR-codes in the “Link a new device” section of your messengers, and you’ll be good to go.
No, as that only applies to someone “transferring” your account to a new device, as in registering a new phone as the new “main” device for your phone number within that messenger, basically taking over your account. That’s a separate attack which the registration lock defends against. This attack isn’t transferring anything, but rather linking a new attacker-controlled device to your account so the attacker get a copy of your messages. Defense against this listed above.
Hope this clears things up. Good luck on your privacy journey.
I’m increasingly of the view that these “super high privacy/security” niche products attract attention to individuals to honeypot levels, even if they’re not technically honeypots - but yeah creating a purportedly super secure messenger that sounds attractive to criminals and then “securing” it using an unencrypted mobile service that authorities in many (most?) countries have open wiretapping access to, doesn’t help with its whiff of honey.
You could be alert to the “you just logged in” messages that most of the services have but of course it’d only take a few seconds for the attacker (be it law enforcement or someone else) to grab what they need before you question it and kick them off
The phishing case is different of course. Anything can be phished.
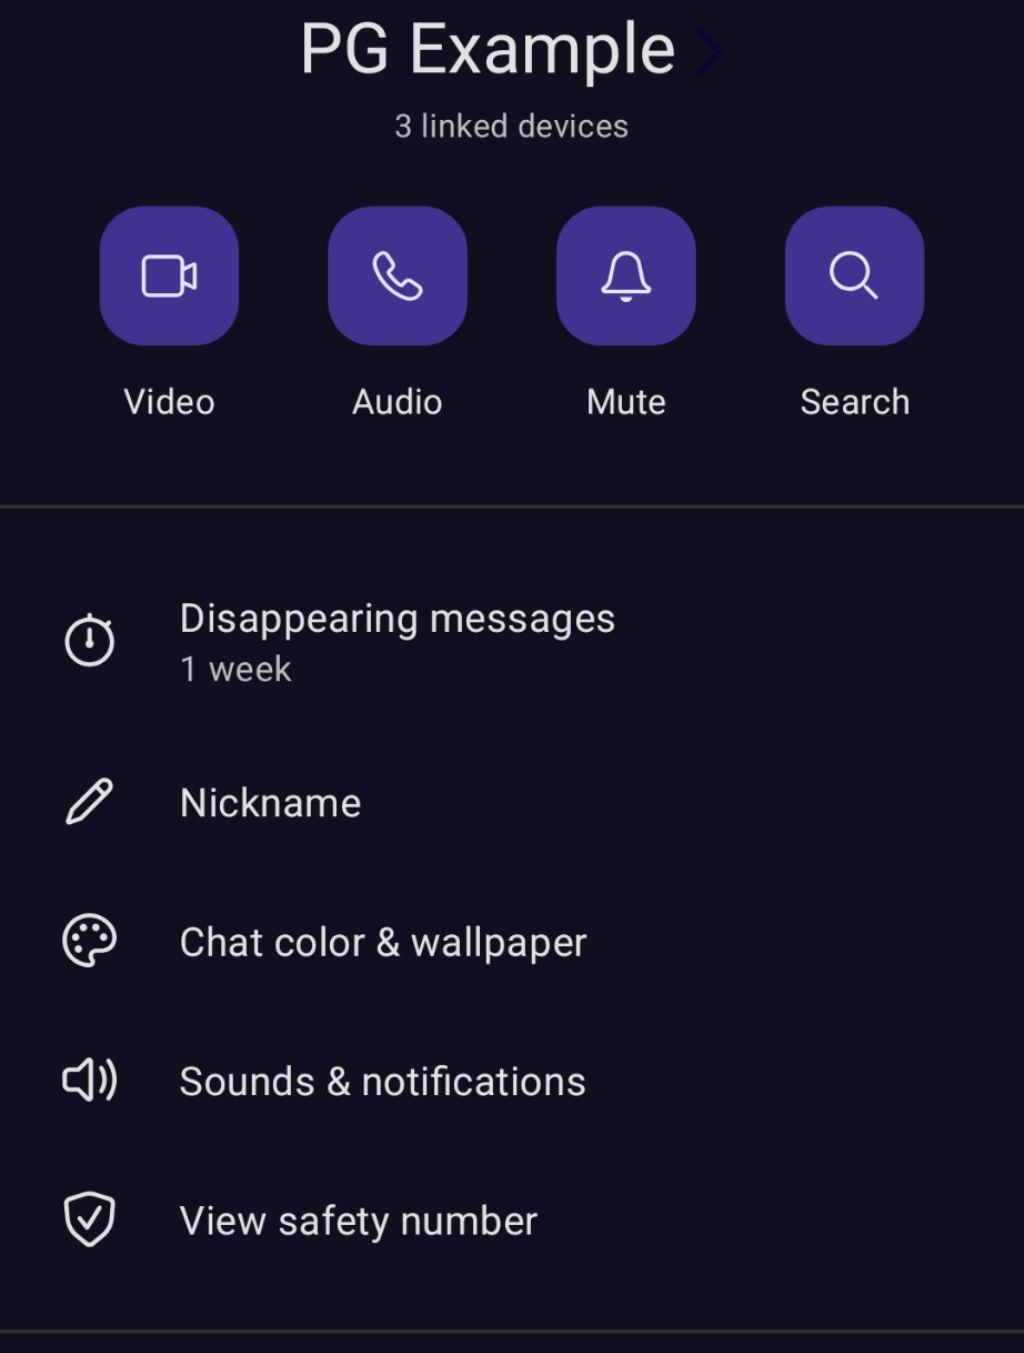
Molly has a feature where it shows how many linked devices a contact has. I don’t think it shows you how many YOU have any more easily, but for your contacts it does.
So I suppose in this context, Molly can be helpful to see if those with whom you are chatting have recently added a linked device, so you can confirm with them.
Note: Molly does not notify you at all, so you’d need to manually note the linked devices and check periodically, it’s far from ideal, but offers something that Signal does not.
Like @Bluetacked points out, it’s suspected authorities often have the ability to intercept or read text messages. In that case, it doesn’t seem like the user would have to make any mistakes for this attack, and it’s essentially a guaranteed backdoor. Am I missing something?
I may be judging the rest of the world by UK standards but pretty sure they have open, warrantless access to SMS (and calls) here and would be surprised if this doesn’t apply to quite a few other countries despite ours being one of the worst for surveillance. Correct me if I’m wrong.
That’s a different attack entirely. The attack in the article is about getting an attacker-controlled linked device to a target-controlled account without the target noticing, and thus getting a copy of all future messages of that target account. It’s aimed to be sneaky so that the target isn’t alerted to the fact that their messages are being intercepted.
A straight-up SMS 2FA token theft would be a full account takeover. Whoever stole the 2FA code could then register their own device as the new “main” device, taking over your account. The problem is, this kind of attack would de-register your previous “main” phone instantly, thus alerting you & potentially your contacts (through the “security number changed” messages in-conversation) that something is wrong. It’d be a very blunt & obvious attack, which would most likely mean that the target figures out that they’re being targeted, thus upping their security afterwards.
And besides, that’s what the registration lock defends against. If the attacker captures your SMS 2FA codes but doesn’t know your registration lock code, they can’t take over the account.
Is this segment of the article incorrect then? It very much makes it sound like this is the exact attack they are sometimes using. (I know there is also a separate phishing attack.)
German customs officials have been using the web client of different messengers like Telegram and WhatsApp and logging in with the suspect’s phone number. The unencrypted SMS code that’s sent for authentication can then be intercepted by law enforcement to log in to the account.
I got that from the Netzpolitik page, although I had to use my browser’s translation to read it. This is what it translated to:
How the law enforcement authorities “around” this process depends on the technical design. For example, if a confirmation code is sent unencrypted (e.g. as an SMS [Fn. 95]), the confirmation code can be intercepted and used by means of telecommunications monitoring.
While I can’t say for certain, it wouldn’t surprise me one bit. The general non-technical publications with non-technical writers tend to get these kind of details mixed up. And I doubt the writers were given any actual, non-public behind-the-scenes info about the actual attacks. It wouldn’t be the first time either, unfortunately.
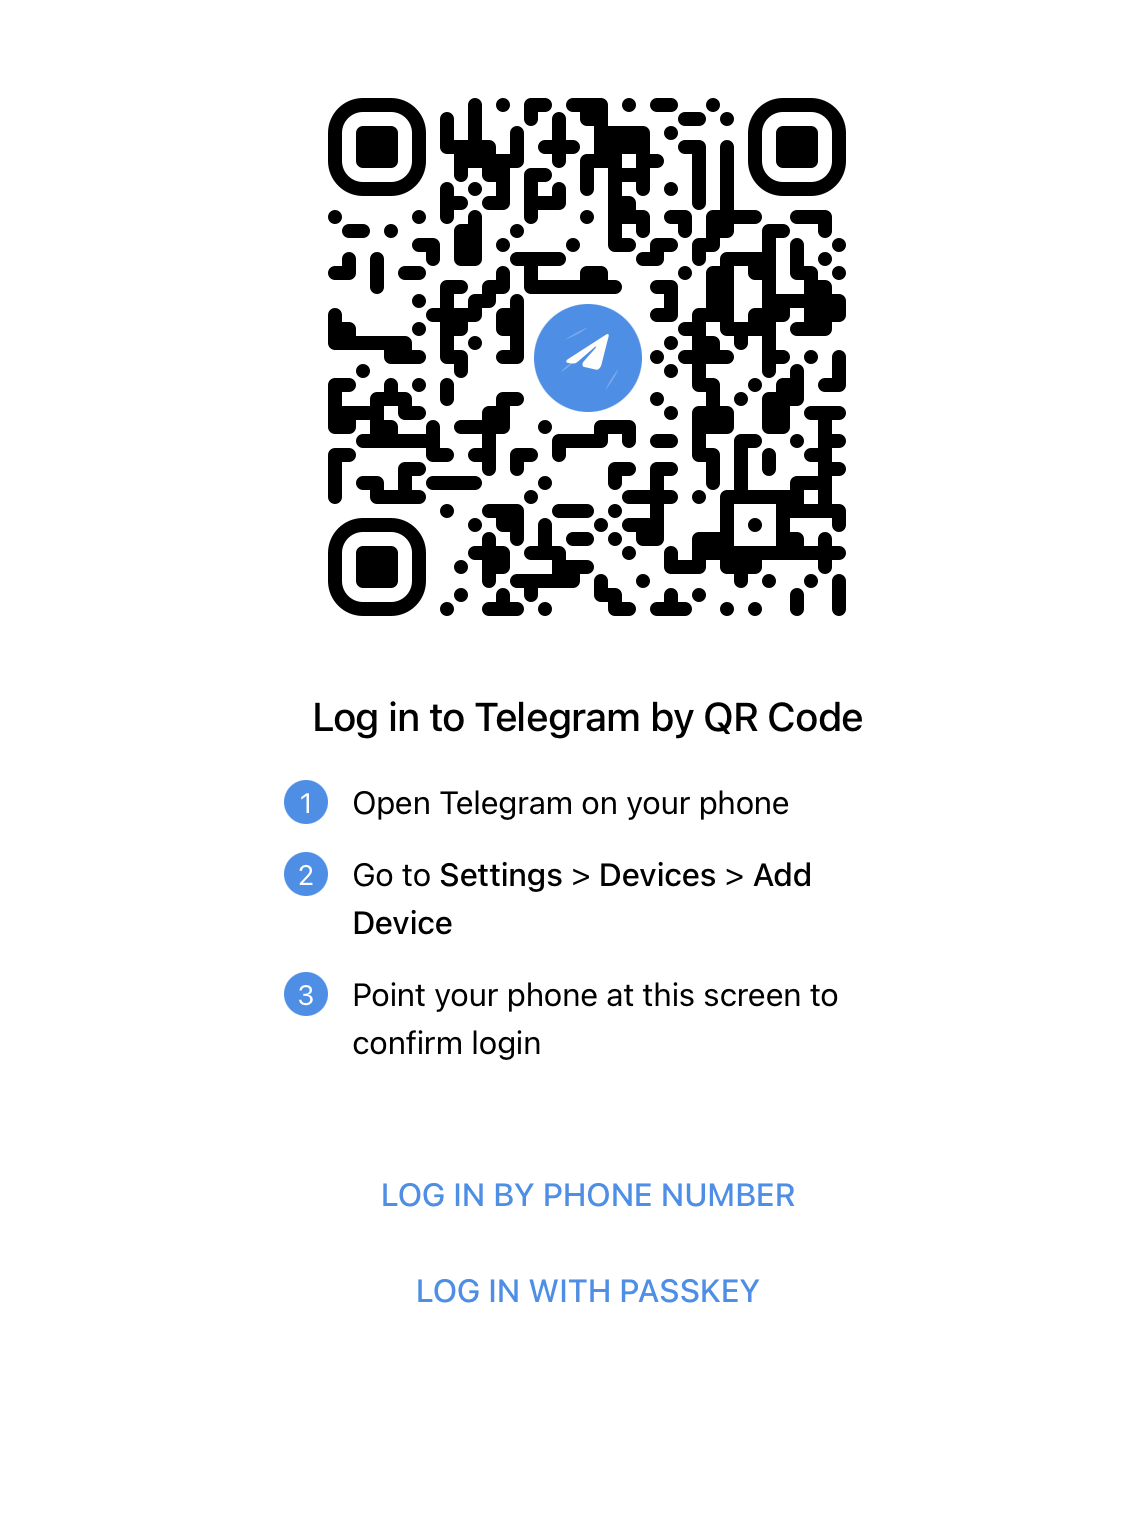
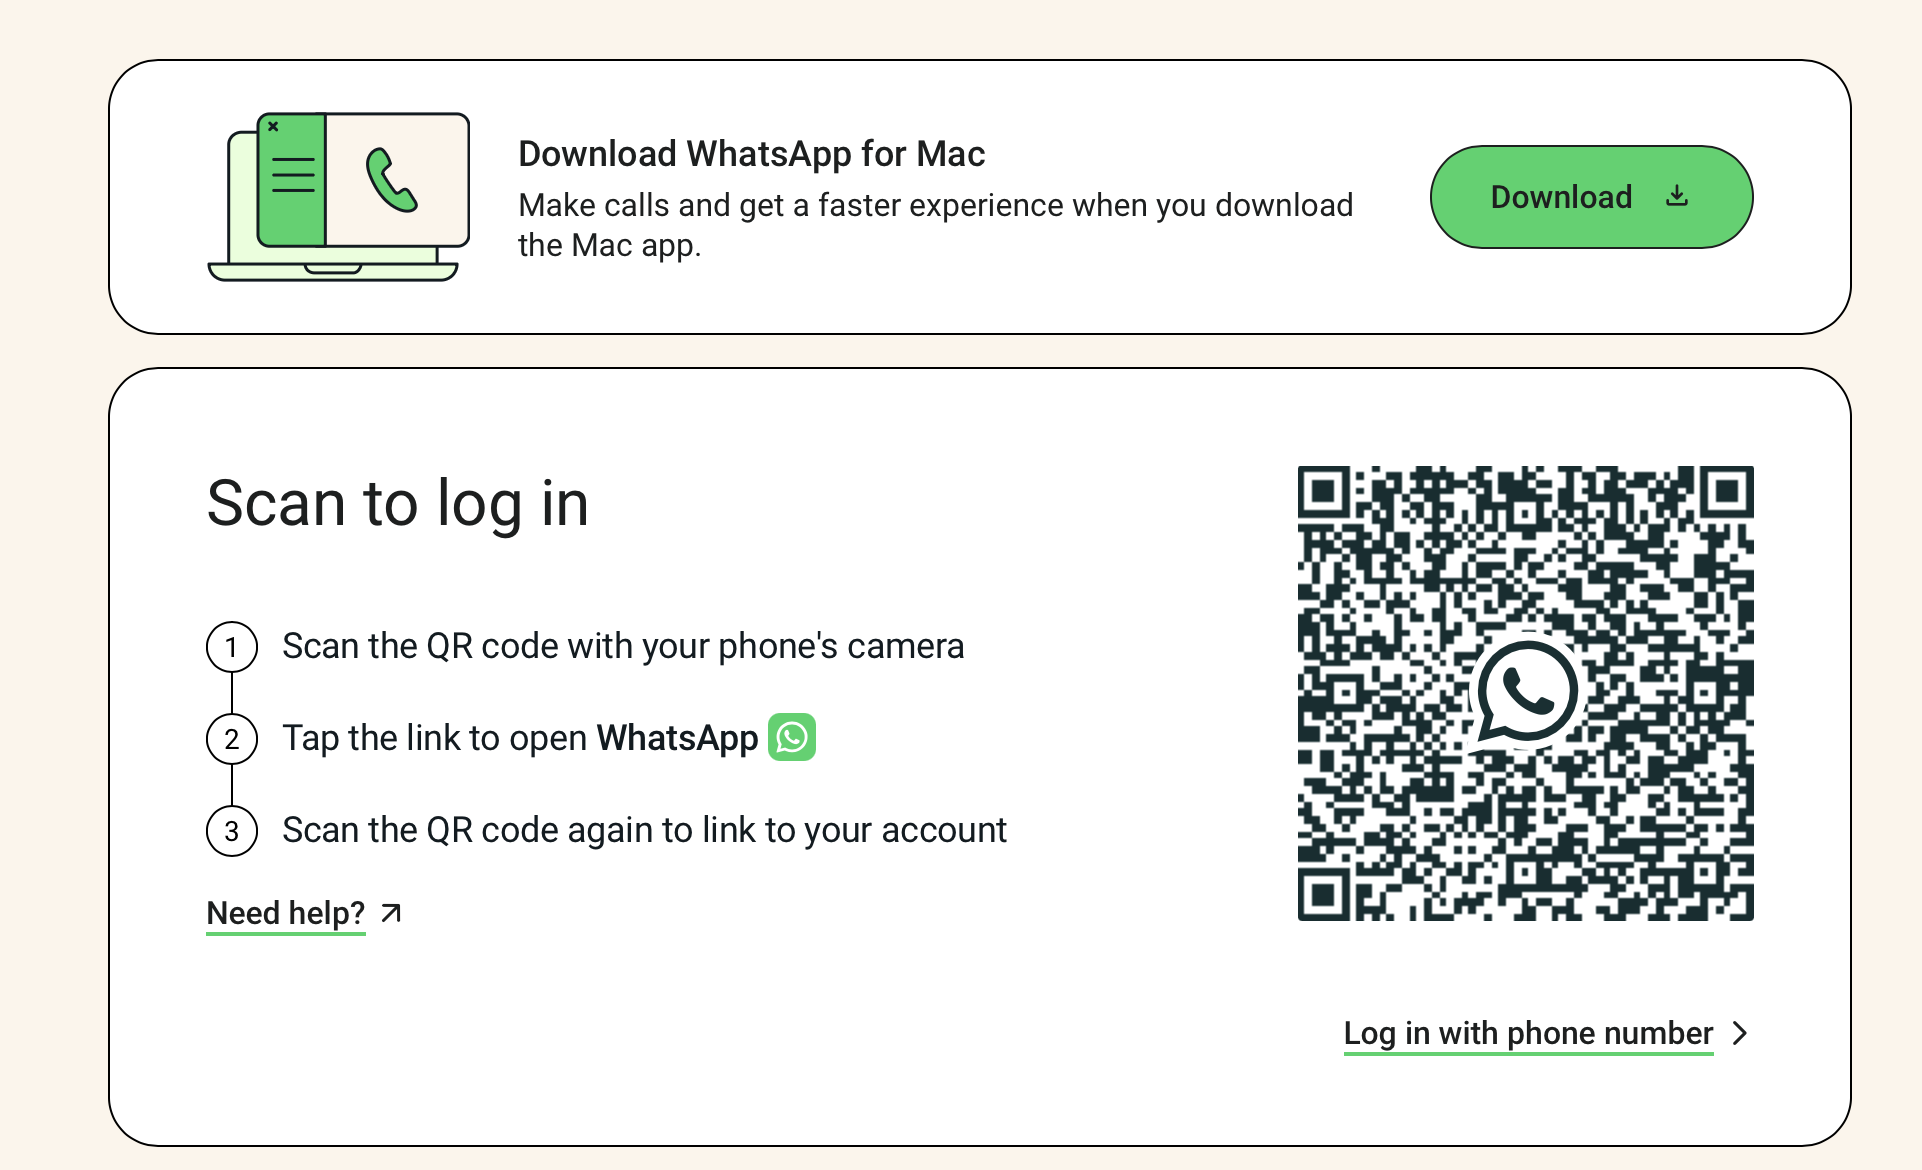
If we take a look at a few popular modern messengers, such as WhatsApp (), Signal, and Telegram (), all of then require the user to scan a QR-code to add a linked device. The SMS 2FA code is only available if the user wants to transfer their account to a new “main” device. While yes, I haven’t gone through all the messengers to see if some of them allow linked devices via SMS 2FA instead of a QR-code, I believe my point still stands.
Tl;dr; I believe the article’s writers got the technical details of two different attacks mixed up.
WhatsApp’s version is more robust because you actually have to initiate the device linking from the app, they can’t just send you a code and ask you what it is. Their version also doesn’t go over SMS, so maybe it’s inaccurate to say. I might have to edit the article to change that.
Signal does seem to require you to scan a QR code to link a device though.
I think you’re right, the SMS attack seems to be an account takeover attempt vs the type of attack the German government is carrying out. I’m not sure why Netzpolitik mentioned it.

 ), Signal, and Telegram (
 ), all of then require the user to scan a QR-code to add a linked device. The SMS 2FA code is only available if the user wants to transfer their account to a new “main” device. While yes, I haven’t gone through all the messengers to see if some of them allow linked devices via SMS 2FA instead of a QR-code, I believe my point still stands.