Hi
Is use Ente auth
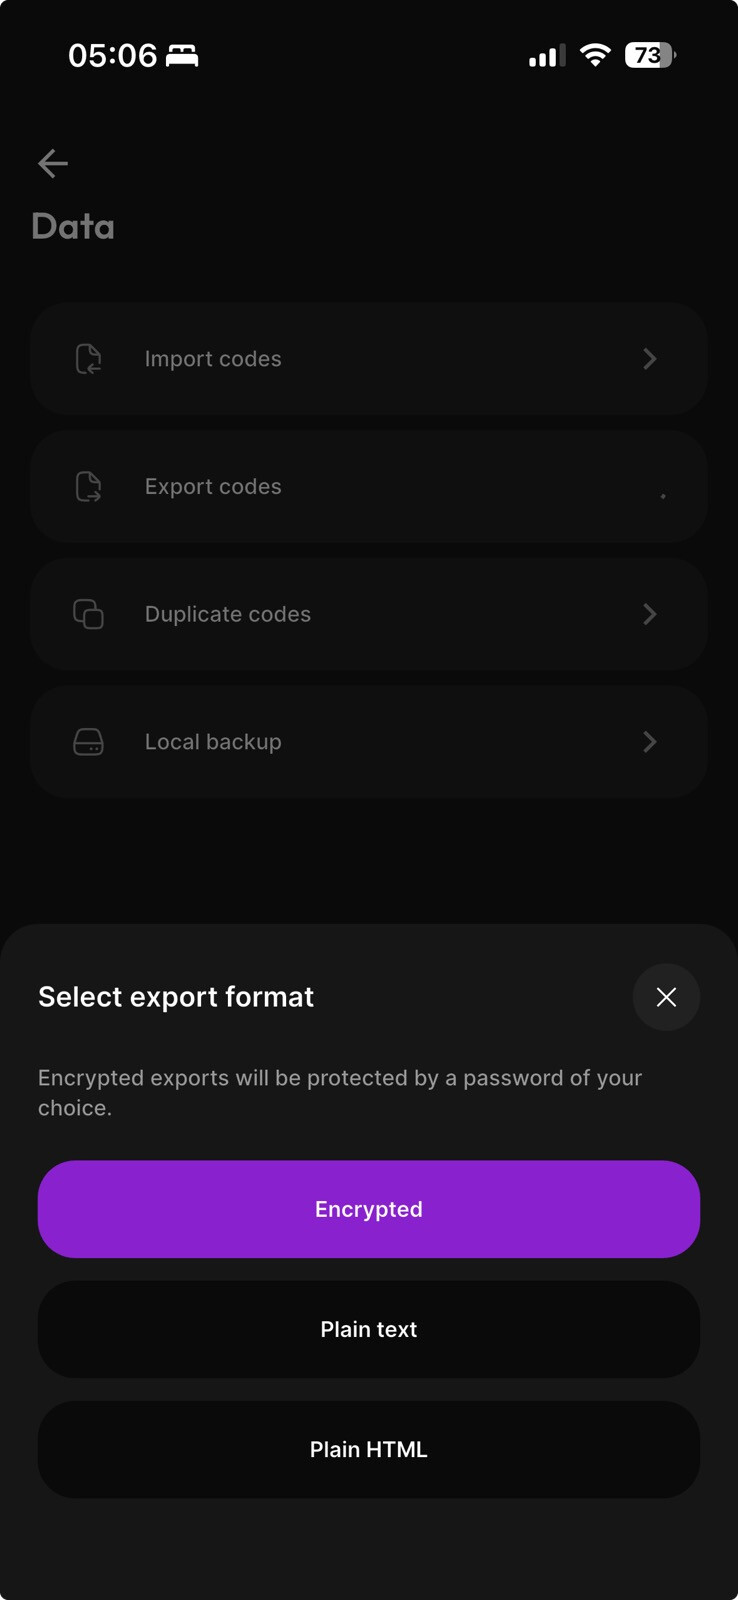
Is Encrypetd “export codes” secure? Can I store it in private Git repo (Codeberg)?
I don’t think there’s anything insecure about the encryption they use, I would just make sure the master password is secure. Any reason you want to store it on a Git repo instead of a cloud account of your own? eg. Proton, email it to yourself on Tuta, Filen etc.
If you want to be extra paranoid, you could attach the encrypted back up from Ente into a kdbx vault through KeepassXC, with Argon2id and then max out the parameters to make it extremely computationally expensive to brute force it if someone were to get an offline copy of it. This would essentially make it so that a truly random four word passphrase would be uncrackable.
From what I read in the repo, Ente already use Argon for backup encryption, though there are differing opinions on the optimal combination of parameters