This is a pointless discussion that keeps circling back to the issue of guarantees. You’re essentially giving the provider free publicity by pushing it to the top of the Privacy Guides forum. If readers visit this thread, they’re very likely to go to the official website and find the services they might need.
2 Likes
Maybe this is how viral marketing works in 2026 lol
5 Likes
Anyway so I just went and signed up for their service. I think their responses are 100% solid. Moreover, they have shown a lot of patience towards OPs incoherent ranting, which means the customer service should be top tier, as well.
So yeah, I guess this is 2026 marketing doing its job.
2 Likes
That’s very common in industries.
In this context, it generally covers what I’ve been talking about, not just “warranty.”
“Advertising”: This isn’t free advertising on my part—it’s the opposite; it’s advertising for the forum.
However, when you confront a company by questioning its vulnerabilities, what happens? The outcome varies.
Here are some questions to analyze these companies more thoroughly (depending on the person’s ability):
1. It’s not about whether it’s true or false (“binary”); it’s: Do they mix truth with lies?
2. It’s not about whether their words sound nice; it’s about whether they have irrefutable evidence for their claims based on real facts? ← This is one of the most challenging questions for any industry, regardless of category.
3. It’s not about whether it’s safe; it’s about: What are they hiding behind their actions that aren’t visible to the public? ← It seems like a simple question, but in reality, it goes beyond “complex.”
4. … (continued).
A concrete example: A company claims that one of its products is “state-of-the-art.”
What do I do? It’s very simple: I take those words—“product” and “generation”—compare them with the rest of the industries across different categories (whether online or in real life), and see that it’s nothing special. Free advertising, at the very least…
It’s very simple for me because I already know how they operate.
If anyone is interested in learning more, start an off-topic thread and I’ll help you out.
1 Like
NYM HAS BEEN CAUGHT FOR THE SECOND TIME
Previously, NYM had stated “Privacy Guaranteed,” but it turns out they changed it by hiding the word within the following box:
Independently audited
Annual audits and technical reviews ensure the network is transparent, secure, and log-free.
-> What they’ve done is build in a sophisticated trap, and instead of improving, the company is getting worse.
Take the mafia, for example: if they defy what they call “impossible”—which is a huge lie—and something happens to a person with a family while using their VPN service, that family can legally sue NymVPN.
When people eventually decide to realize how these companies operate behind their rhetoric, they’ll run away, and Web 3.0 will decline drastically.
The latest messages from Carsey Ford (admin) and Alexis (COO and co-founder) tried to draw me into a game of cat and mouse. It’s their responsibility, not mine, and I’ve been quite clear in my messages.
Below is the latest update and the real battle—but with a clear warning to the company:
- (Yo) DanielM:
@harryhalpinharryhalpin
Greetings.
I’m reaching out to ask for an update on whether the information on your website is currently accurate or if it has been altered for another purpose without your knowledge.
The phrase “privacy guaranteed” no longer appears on your English-language website; it now reads as follows:
Independently audited
Annual audits and technical reviews ensure the network is transparent, secure, and log-free.
Is this correct, or is there another intention behind it?
- CEO Harry:
I didn’t remove that phase but maybe @sallysundriesur editor @sallysundries did as I suspect it was written by (our now departed) previous marketing people. However, privacy is a holistic property of a system, it can never be guaranteed like security can.
- Casey Ford (Admin):
“Independently audited
Annual audits and technical reviews ensure the network is transparent, secure, and log-free.”
Is correct. The change was made to be honest with our users about the specifics of how Nym protects you concretely rather than through marketing claims. The guarantee is a network that can’t log your full traffic by design.
- CEO Harry:
An explanation by me is here - see Section 3 https://www.ndss-symposium.org/wp-content/uploads/usec2021_23007_paper.pdf
However, we CAN guarantee security claims via formal verification and we will have an exciting blog post on that today, as we are now formally verifying our core code.
For an explanation of formal verification by myself, see here: Making sure you're not a bot!
- (Yo) DanielM:
@harryhalpin @sallysundries
I’ve analyzed your arguments to a certain depth (not exhaustively). Before continuing, I’m letting you know up front that I didn’t come here to be gifted a license (dVPN), a job, validation, etc. I came to find the truth behind what is “superficial” within the company, not to destroy it, but to show that the advertising is bigger than what you claim.
Harry, I understand what you’re saying and I’ve read some of your messages when you mentioned those cases here in your Telegram group.
The new claim has a sophisticated trap (probably the person who made the change doesn’t know it) and it is the following:
- It explicitly guarantees the following words, literally covering 3: transparent, secure, and log-free. However, guaranteeing security and no logs also encompasses privacy; without the previous two, there is zero privacy.
There’s the real trap, the word privacy is hidden, not implicit.
On top of that, that new argument raises even more suspicion and doubts about the company itself.
I ask you the following questions:
- Why don’t you permanently remove the word “guaranteed” and be more honest?
- Suppose you insist on keeping that word, what will you do when it fails one day? Will you be ready to face real lawsuits if they file them?
- I’m still interested: how does the company Nym defend legitimate people against real adversaries when they use the nodes? Will it be the fault of the person using the service, as Nym’s terms claim, if something serious happens?
- …
In the following URL: NymVPN Litepaper: Decentralized VPN & Mixnet Privacy | Nym
There are many claims in relation to it…
Note: I will copy and paste the messages into the Privacy Guides forum so that people know more information about the company itself.
- Casey Ford (Admin):
I’m not sure I understand, so feel free to clarify if I am not answering your question properly.
We have removed the word “guaranteed” from our landing page where it originally appeared as a marketing claim from a previous employee as “Privacy guaranteed,” referring to our policy of conducting independent, external audits of our services.
The reason we removed it was because we felt this wasn’t a good use of language. Privacy is not something that can be “guaranteed” by any one service. For example, while NymVPN can help protect your privacy at the network routing level, it can’t stop you from deanonymizing yourself some other way, or stop all forms of surveillance.
Ultimately, the edit on the website pertains to that particular section of the landing page. What is currently claimed accurately is that:
- Nym is committed to performing audits of our apps and code by independent, external researchers and security firms so that they are continually improved for users’ privacy.
- That the code remains fully open source so that it can be verified as doing what we claim it does
- And that the decentralized network is designed so that Nym never has access to your traffic at all, and node operators never have access to the full route your traffic takes. This makes full logs impossible to be collected from any single point. This is a network design, not a marketing promise.
I’m happy to explain any part of the Nym system or marketing claims if you have specific questions! Just drop them here.
Our goal is honesty and transparency and education, so if you do find claims that are inaccurate, we’ll definitely investigate and correct if needed. Many of us are academics, we’re use to it! 
- (Yo) DanielM:
Is the man named Alexis Roussel on your team aware of this serious problem? According to Nym’s official source, Alexis is Nym’s COO and co-founder.
This sophisticated scam reveals that the company itself is not internally aligned, and your behavior speaks volumes. It is, therefore, highly suspicious and actionable (a family could sue Nym for false advertising and deception if something happens to them due to real adversaries through its network). This covers any “threat model” regardless of the level.
Didn’t your lawyers tell you this?
You say you’re willing to explain it to me, but I asked questions about Nym and everything surrounding it—how do you explain it to me? The questions remain unanswered.
Be truly humble and honest.
Harry: Are you aware of this issue, since you’re the CEO?
- Alexis Roussel (COO Nym):
Not sure what you are trying to say, but the wording on the website is correct.
- (Yo) DanielM:
If that’s true for Alexis, then in the future they won’t be able to say, “Nobody told me.”
- Casey Ford (Admin):
We are not understanding you at all. 
- Alexis Roussel (COO Nym):
Yep. Sorry we don’t understand.
Maybe you can be more specific or detailed?
End of messages.
Keep the following in mind: NymVPN has no real evidence against real adversaries; it’s all just probabilities, which means → luck. Regardless of the level of the “threat model.”
If something happens to you while using NymVPN, remember what’s been said here.
1 Like
Your logic is just fundamentally wrong. Stating you have two properties A and B that potentially contribute to C does not inherently mean or imply you have property C.
They are claiming that their service is secure and log-free. They are not claiming that they can ensure privacy, and they explicitly said that in the chat logs you posted.
Your focus on this one section at the bottom of the page is also just extremely bizarre.
4 Likes
HARRY (CEO) PUBLICLY CONFESSES THAT “NO ONE CAN GUARANTEE THE ABSENCE OF LOGS”
His lethal contradictions condemn the company itself with his own words, but, at the same time, he is telling the public the reality that something serious is happening internally within the company.
What is happening? is a deep question, but I don’t have the fundamental data since I don’t have internal access to the company. Nevertheless, Harry and Alexis are two extremely contradictory individuals (both confessed publicly).
Possible strange question: Is this a game, or is what’s happening actually serious?
I’m inclined to believe it’s real.
The website has heavily inflated and highly deceptive advertising, not just in one single place called a “guarantee.”
Unfortunately, I haven’t been able to find that “person” right now who, according to Harry, was expelled, in order to get their testimony. It’s highly likely that this person doesn’t exist; it must be an excuse to make people believe in something that currently has no basis. Does a person exist or not? With so many contradictions between the Nym team and its website, suspicions are extremely high.
They kicked me out of their Telegram group; on the one hand it’s better, because it reveals more of what they say.
Casey Ford (Admin) replied to me when I responded to Harry, but I ignored him; it’s just noise now. I don’t know if he’s aware of, or oblivious to, the true knowledge of the military’s technological force regarding its advancement and what exists in private (not visible to the public).
Below are the messages between Harry and me:
- Harry (CEO Nym):
No one can guarantee zero logs and anyone that says they are “guaranteeing” zero logs and so forth is lying. A adversary can easily log information such as timing and volume WITHOUT even having to compromise a machine. Nym solves that by decentralization and adding fake traffic/timing delays (i.e. mixing). Also, for any centralized VPN, a govt. can force a backdoor (and even make it illegal to talk about it or ask a lawyer, see FISA national security letters and the Nick Merrill case).I have no idea what you mean about “new claim” but technology isn’t magic, however, we do think we do a better job than any centralized VPN or even Tor in defending our claims technically. As for word choice issues by our marketing people, we fired the guy that wrote some of it as he wasn’t very good, and @sallysundries can sift in. If anyone wants to run a node, they surely can - that’s decentralization. No one needs a license. That being said, if you don’t want to run one and aren’t comfortable with the legal risk don’t run one.
To repeat: Privacy is a holistic property. Transparency is gained by looking at source code, compiling it yourself, and so on. In terms of security, it’s always relative to an adversary, and Nym and mixnets in general are built to combat a global passive adversary that watches every packet and records it. Others may think this adversary is unrealistic. See here: https://academic.oup.com/cybersecurity/article/11/1/tyaf006/8097877
- Yo (DanielM):
Exactly, and your website says the opposite about the logs—why didn’t Casey update it at the time when he removed the rest and added new text? Read on below.
Audits won’t help you down the road, Harry; those guarantees stated on your website are the company’s downfall:
- Down the road, a zero-day exploit could emerge and compromise something—for example, security.
- An APT may or may not have been operating on your network of nodes for some time, adapting in real time.
- The NSA (as well as other authorities in other countries) is dynamic and possesses technology that neither Nym nor the public is aware of; therefore, it’s unclear whether the “mixing” is still useful, only partially effective, or, in general, just a matter of probability (luck).
- etc.
Your nodes are also vulnerable and could (if they currently exist) be compromised by sophisticated malware, and the people who connect to them could be affected. That’s the reality, Harry.
The point I’m making is that that part of the site is rife with misleading advertising (the URL cited earlier in my response). You’re speaking technically, but someone with a high level of cybersecurity expertise and knowledge of real-world facts wouldn’t say the same thing. You’re being too overconfident.
Can you tell me who that fired person is (if they even exist), or is that confidential information? I’m interested in hearing their account. What I see here is that the company itself isn’t on the same page, and the problem is obvious from the outside. Suspicions are already running high.
And my questions remain unanswered.
For the record: I’ve reported the matter to the FTC and SECO.
End of messages.
Why haven’t they answered me yet, not even question 3 (how does Nym protect people from real adversaries on its nodes) that I asked, and neither of them responded? It’s very simple: their terms of service put the blame on you:
- If an exit node logs your data or manipulates your traffic, for example: advanced phishing… It’s your fault, not the company’s.
- If a node logs your IP and sends it to an unknown destination for real-time monitoring with all data included, whether encrypted or not, it’s your fault, not the company’s.
- If the mob hires adversaries with APT (Advanced Persistent Threat) capabilities among the nodes and something happens to a genuinely innocent person within 4 weeks, it’s that person’s fault, not the company’s.
- … (continues).
Don’t trust NymVPN; if something happens to you later, they’ll blame you and the company will wash its hands of it. Of course, you have every right to report the company for fraud and public manipulation, but you need irrefutable proof of what happened to you.
I’m going to translate the complex into universal human language so that people can better understand this situation, especially those without prior knowledge:
- The NymVPN company has revealed its internal instability in front of the public. This means they are out of sync and make terrible mistakes, such as: deceptive advertising.
- Harry, the CEO, trusts more in technology than in being virtuous (humility and sincerity). He might change later on; sometimes, you have to give people time.
- The company’s best defense is “FUD” and its technological complexity. Debating on this ground requires time and knowledge. A person who is unaware of these simple tactics is vulnerable; if they accept things blindly without questioning, they will lose quickly.
- Harry and Alexis have shown they are out of sync; they are two high-ranking individuals in the same company. According to official information from Nym on their website.
- Is it safe to use their service? It depends on who you ask. The real question is: is it worth what they claim? Not for me.
Straight to the point: I simply brought Nym down from its own “throne” to reality itself, so they could see themselves and who is who. What they do afterward is their responsibility, not mine.
Fundamental note: after having read this, if you decide (supposedly) to buy a subscription and keep using the service, what will you do if your personal data is leaked to the best impostor or your traffic is manipulated for such malicious purposes?
You decide what to do.
Today, 09/05/26, the official Nym website in English has been updated.
The homepage has undergone a fairly useful and streamlined change, so I’ll offer a brief observational analysis:
- They’ve featured Edward Snowden as a selling point to further boost “trust” in the Nym service.
- They’ve created a 4-step process to get started with the service. Each step has its own focus, according to the writer’s argument.
- They’ve included animated graphics to help explain the software’s inner workings and capabilities.
- They’ve removed the word “guaranteed” and its synonyms. Only “Independently audited” appears. Below that are icons linking to related information. For now.
Recommendation for Nym on the homepage:
- Include a link to documentation explaining the software’s actual functionality for people with no computer knowledge.
Critical risk detected:
- In step 3, the writer used the word “lovers.” In this context, the company assumes or implies that it already knows all or some of these “people” who manage the nodes (servers), revealing who is who, including malicious actors. How does the company know about this? Is there something the public doesn’t know? Why does this contradict the operators’ own terms, such as Sessions II and IV, for example? Is it possible that an AI (machine) is managing a node rather than a real person? …? On Android, the app lists 73 countries with 593 nodes, not the 800+ nodes stated on the official website. Unless there are reasons related to limitations such as “not affecting the app’s performance,” this discrepancy isn’t explained and could be considered misleading advertising.
Q&A Session:
- What is the purpose of this report? Why does it sound destructive or somewhat aggressive in certain circumstances? Answer: It’s simply to help people not fall for “smooth talk” and to reinforce their approach to communicating with a company, regardless of its status. And if I wanted to be destructive toward Nym, I would have done so from the very beginning, surgically and irrefutably, letting it destroy itself.
- Who are you, and why do your mannerisms sound like those of a high-ranking military officer or someone who works for an agency, for example? Answer: Don’t focus on my “credentials”, my actions speak for themselves. That’s why the vast majority of people fail to understand me. I am independent.
- Are you seeking approval from the Nym company or from people? Answer: No. The responsibility lies with the Nym company for its actions; I told them what I had to say, and the demonstration publicly exposed its real contradictions. You can verify this yourself in the context of my conversation with them on Telegram, the company is internally unstable.
If I want to, I’ll do a comparison review of Nym versus IVPN later on. Time will reveal the truth as it is.
Note: Spanish to English: using the DeepL (AI) translator.
The most important thing first:
I mean, if you know anything not obvious, you should disclose it, no?
I don’t disagree that Nym’s wording leaves a bit to be desired, but that is commonplace in this sector.
(Also, I don’t mean to offend you, but it does seem that the thing you claim wanting not to do is the purpose of this thread.)
They probably don’t and simply mean to say, that running a node makes you a privacy lover in their eyes.
What makes you assume that?
Did you check the app yourself? I saw the screenshot in their website, which also only says “586 servers”. Could a server run multiple nodes? They differentiate the word “server” and “node” on their website.
It could also mean they plan to deploy additional nodes or include more from others, if I understood correctly how it works, and they do not want to update the website all the time.
Offtopic
(Again, I don’t mean to offend you, which is why I put this into collapsible text.)
This probably does not translate very well, as it seems to brag. Maybe the “vast majority” does not understand because of a culture or language barrier.
Please do, as it seems you already have a lot of effort to understand it.
But my I ask about including Proton and Mullvad, too? They still are recommendations here. Maybe a more general comparison between these three and Nym makes more sense.
That all being said, although I’m not interested in Nym right now, I have been curious.
Here is my response:
- I have pointed out a few, for example: requesting irrefutable evidence of the “guarantee” against the NSA at the technical level, based on real-world facts, not laboratory conditions. Requesting this evidence, implies, at a minimum, that the NSA participate in such real-world tests in conjunction with the company Nym, etc. Since this isn’t happening, the guarantees fall apart on their own, and the “theoretical” technical level collapses on its own. Logically, the NSA isn’t going to participate, it’s that simple, and if they ever do, it will be for their own purposes (based on their current strategies and tactics) and not for the participating company; that would be quite rare and unusual, and suspicions would run high in such situations if they were to occur.
- You’ve misunderstood me. The author who wrote that word along with its context, as stated on their website:
3 - Choose your decentralized path
Choose your entry and exit servers. The Nym network is decentralized and run by an independent community of privacy lovers.
Servers in 70+ countries
800+ nodes
Residential IP support
As you can see, it says “independent community.” By including the word “lovers,” the situation gets even worse, because it goes against the operators’ own terms, against decentralization, and against “independence,” at the very least—and this raises questions: Who writes those messages on the Nym website? Who approves them without knowing the problems that arise elsewhere, including with “legal documents”? etc. If it were independent, it wouldn’t be subject to Nym’s operator rules; adversaries could freely pose as defenders of “privacy” (the mafia, the NSA, the CIA, and any other real adversary engaging in such acts according to their intentions), ignoring even Nym’s own terms, among other things. The truth is that the more problems there areas you say, “common” ones that are actually serious, the more adversaries, including novices, can exploit all those corporate vulnerabilities and pose as sophisticated Crypto AG-style companies (behind which the CIA has been, for example) that have been operating quietly for years. Is this really what people want?
I’m not making assumptions about AI, I’m asking. It’s a valid question that has profound implications for many things, such as a script, for example.
Yes. As verified at that moment, how that number changes is not something under my control. Here’s a screenshot, even the “inbound” and “outbound” numbers are the same without the QUIC protocol enabled. The IP is static when you connect to that outbound node; in Mixnet mode, the number of nodes changes, differing from Fast mode:
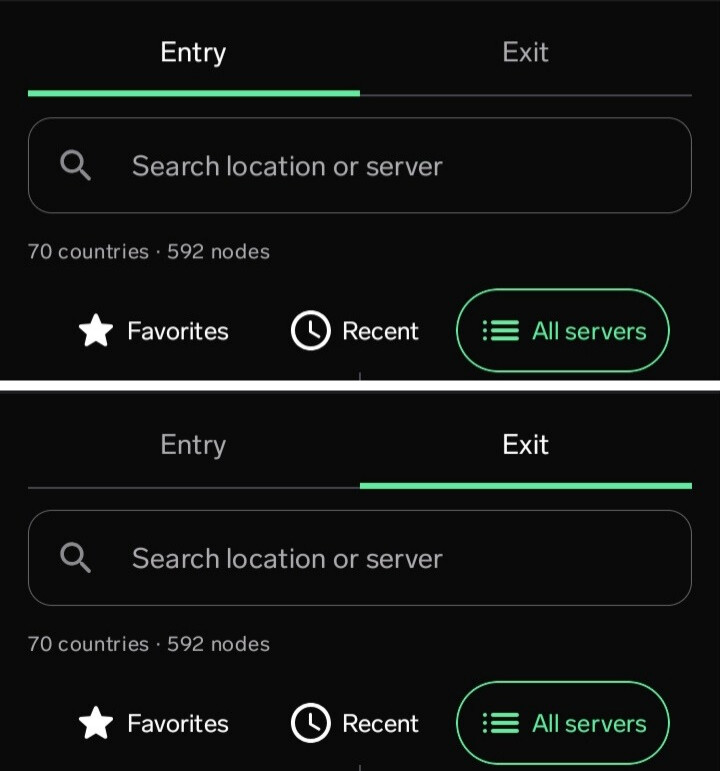
A server is a node, depending on the application in fast mode. In fast mode and Mixnet mode, they have the same static IP addresses on the same node; the difference is that when you select Mixnet mode, the number of nodes (servers) suitable for this configuration is filtered and reduced. You can verify this yourself in your client.
More official information here: Essential Parameters & Variables | Nym Docs
- It’s not a language or cultural barrier. It’s my operation: technical level, legal level, user level, physical level, and whatever else is relevant, all processed simultaneously, not just one at a time. That’s why many people can’t understand me.
- No. IVPN is the right choice, and it’s what I truly recommend. When it’s available (if it is), you’ll be able to use that comparison against ProtonVPN and Mullvad, without needing to delve into lengthy details involving multiple companies.
I understand your curiosity, but the facts are laid out, and you can read them for yourself; it requires active engagement and knowledge across multiple areas to understand them deeply. If you read superficially, you won’t be able to understand my messages, at least in most cases.
This is the most ridiculous complaint in this thread. If it wasn’t obvious you’re just targeting them before, it’s extremely obvious now.
2 Likes
Refute my arguments completely instead of attacking me personally, and if you didn’t know or forgot the rules, I’ll help you remember them:
Be Agreeable, Even When You Disagree
You may wish to respond by disagreeing. That’s fine. But remember to criticize ideas, not people. Please avoid:
- Ad hominem attacks
If you have solid, irrefutable arguments (which you haven’t provided at any point so far in any of your messages), make them known; if not, the rules apply to you.
What’s important is that the company Nym has acknowledged (hopefully that’s the case) regarding the word “guarantee”, that they haven’t been able to uphold it, because someone who actually works or has worked in cybersecurity, intelligence, and counterintelligence knows very well that it’s not possible to uphold that claim. If Nym genuinely acknowledged this, that’s a positive development, and honesty is valuable, and that’s what I’m looking for, not a string of “lies from one company to the next.”
1 Like
Just came out to say that Harry seems like a good person. He is very accessible, I met him at a privacy-focused conference, and he is quite accessible and even introduced me to a few persons, which was nice of him
I also would like to say that the loaded language of OP, combined with text in uppercase, feels like Clickbait and doesn’t really make me want to read it in full. (Don’t take it personally, but in life if you want people to take interest in what you are saying, seeming angry isn’t the best strategy)
Finally, I think that Nym problem isn’t the technology, it’s positioning. Proton VPN is geared toward the general public that is also privacy-conscious, Mullvad towards the privacy-conscious, anonymity-wanting and IVPN is geared towards more tech-savy users and more affluent.
I don’t really know towards whom NymVPN is geared towards.
And it’s expensive, like I checked and realised the prices displayed in website are without VAT. They should offer a free trial, without payment details (maybe do 4 days free every 3 months on specific date, up to x thousands account to avoid DDOS.)
This isn’t an “attack” on you. Complaining about a privacy company marketing a privacy product calling the people who use or contribute to their service “privacy lovers” is just ridiculous. It also has no impact on the “independent community” phrase, since it’s quite obviously an assumption based on the purpose of the product.
Likewise the complaint about calling it an “independent community” makes little sense either. They operate a dVPN/mixnet. The entire purpose is that there are a bunch of random people that Nym the centralized entity knows little to nothing about running most or all of the nodes. If Nym had to manually approve these applications, it’d defeat the entire purpose of having a decentralized network. They have terms that operators are supposed to abide by, but they cannot tell if there’s a violation unless they are reported or somehow noticed while doing something wrong (at which point the node can be blacklisted in at least the client through an update, not sure what other means they currently have). Presumably you are familiar with Tor. Tor has the same issue. They can try to reduce the problem by having node reputation (which AFAIK Nym has as well) and so on, but fundamentally the networks require unknown people to run the software on their servers (which could potentially be maliciously modified by the node operator). This is a pretty much unfixable issue with this model, but it’s a tradeoff to avoid having all your trust in the network being placed in one entity (the VPN company) in normal centralized VPNs. Whether they’ve done enough to mitigate that issue is up to you to decide (which you very clearly did before you even created the thread).
Regarding the number of nodes being reduced in mixnet mode, presumably that’s because operators can choose what to provide. In other words, they can provide mixnet nodes, just dVPN nodes, or both. IIUC they can control whether they provide exit gateways for instance as well. I haven’t bothered to check the numbers, but if there’s a difference between the number they’re reporting on the site and the max of both modes, then it’s likely because they’re counting all the nodes (individual dVPN + individual mixnet + both dVPN/mixnet) in that number.
In any case, you keep reviving this thread. If you weren’t targeting them, you’d have said your piece and been done with it after the initial discussion where you claimed to be “closing the matter” three months ago, but given that you were apparently on the Nym Telegram over a month after you’d made your thoughts clear(-ish) and then posted the messages here with an all-caps, bolded, tabloid-like header, and then you just revived it again after another month, you clearly have some bone to pick with them.
3 Likes
Is it actually that expensive? I just quickly checked the prices, and they seem like they’d still be cheaper than Mullvad with VAT (assuming you subscribe for at least a year). The monthly prices are indeed expensive though. Seems similar to IVPN in that subbing for less than a year is probably too expensive. Their homepage says you can get it cheaper if you use $NYM or whatever (their cryptocurrency), so I guess that’s an option, although I’m not sure how difficult it is to get their token.
I’ve got a NYM subscription and had a free trial before signing up. I caught them during a sale and paid something like 60 maybe 70 and got a 2 year subscription. It’s been good so far imo.
I’ll address the key points:
- “…seeming angry isn’t the best strategy.”
-> Use your reasoning without letting your emotions guide you, and you’ll see that’s not the case.
- I don’t really know who NymVPN is intended for.
-> It varies; it’s even intended for adversaries.
If it were “ridiculous” and a “complaint” according to your interpretation:
- Who would dare call an independent community which could be anyone, such as adversaries at any level and one or more machines (AI), if any are currently active regarding (AI) “privacy lovers”?
- Do you know how real adversaries actually operate in this context?
- Is your intention to prevent me from helping the company improve, or are there other motives? Based on your behavior.
- Do you think I’m complaining? No, I’m reporting an issue, it’s very different.
- If they know little or nothing, why have they included those new words (question 1) that even contradict their own terms?
Not Tor; I focus on Nym. Nym is part of Europe, they say so themselves: Built by academics - Funded by the European Union.
They added that to their official website today. What does that mean? If it’s from Europe, then the service they offer is opposed to the NSA, the CIA, the mafia, etc. In what sense? Reread question 1 that I asked earlier and understand it thoroughly.
I accept your limitations in not knowing certain things. However, I acknowledge that you’ve made valid points, such as the allegations about nodes that might behave suspiciously or rather, modify the software for such purposes.
You said: If Nym had to manually approve these applications, it’d defeat the entire purpose of having a decentralized network.
Those words of yours support my argument (Question 1) + context.
Regarding the numbers, it’s likely as you say. Based on my verification, they are the same IP addresses, and according to the documentation I checked on the official site, they are the same nodes suitable for both modes (fast and mixnet, or one of them, depending on the operator). This needs to be clarified because it can cause confusion and could be considered misleading.
It’s true that I mentioned shutting it down, but I didn’t say forever or eternally. There’s nothing wrong with capitalizing a title and providing supporting arguments in the body of the text based on the context. Don’t forget the thread title, which reads: Analysis of Nym VPN…
That’s not a personal attack or a score to settle with them. Don’t confuse being destructive with being constructive, they’re different, and I’ve applied both approaches, even in the Nym Telegram group.
This isn’t “transparency”; it’s realism. It’s not “show me what you’ve got”; it’s me presenting the facts based on reality without fabricating anything (without falsifying messages from Harry or any other Telegram member, for example).
That’s legitimate and public, because people deserve to know the truth and what the CEO of Nym and the other members of the Nym team are saying.
I have more to say, but given what I’ve said above, I’ll leave it at that.
You haven’t presented me with any solid arguments that I can accept.
I’m not a native speaker myself, but I really can’t follow you here. Are they colluding now or not? You seem to say both.
I really don’t want to sound like a prick. But I don’t think you answered the most important points I asked about, e.g. what you’d know what we don’t or what would not align with the general statements. It looks like claims and doubts.
They seem to address the sentiment, not your person. If you deem this an “ad hominem” attack, this would be one, too, if not more than theirs:
And about the “guarantee”:
If they removed the word “guarantee”, would that not mean they acknowledged it being inaccurate in your opinion?
I"m having trouble to see the relevance of AI here, as AI is a mere tool.
As we established, “privacy lovers” is probably meant as a classification for those, who want to provide the service, via a server or a node.
IMO this disqualifies any adversary, because by definition, these would be opposed to the sentiment of loving privacy.
I’m sorry, but what issue? The “guarantee” seems to have been replaced by more careful terms, even possibly by your very own persistence, which I have to admit, I’d applaud you for. Is the whole point not being moot now?
Got it, but if you are not particularly in favor of IVPN or against Proton or Mullvad, why not keep it general then? You would not even have to deal with what IVPN claims, let alone Proton and Mullvad.
Offtopic
I only can speak for myself, but I feel I’m one of these.
What is actually the point, if not marketing phrases?
As I have said before, please provide any insight that you might have, as it could prove useful to anyone interested in Nym. Or at the very least, they could be incentivized to better themselves based on your points and the exposure thereof.
2 Likes
100% does not seem like that is your intention. Seems much, much more like you are targeting them to ruin their reputation.
Perhaps you should think about what and how you are writing if that is actually your intention.
No, you’re really not.
Perhaps this is because you’re translating text and the translation is simply translating the phrase incorrectly. If it’s really translating “privacy lovers” aa “people who like privacy” though, then use your brain please. Do you not know what marketing is? I’m not gonna bother repeating myself.
Marketing, assumption based on core purpose of product. What should they say, in your mind, as a descriptor for the node operators when marketing their product? “Use our service with nodes operated by the NSA, CIA, SVR, BND, mafia, random AI, possibly a few real people, and maybe more (intelligence agencies, of course!)!”
The point was they have the same fundamental issue with their model that they each try to mitigate. Every (vaguely) technical complaint seems to be about the dVPN/mixnet/onion routing model. It is a problem that every network of this type has to try to handle their own way. It is impossible to fully avoid the problem since at some point the request must be sent over the clearnet.
TBH being from Europe does not really mean opposition to the NSA given that European intelligence agencies routinely cooperate with them. Also not sure which “question 1” you’re talking about since this thread is rather long.
Once again, so condescending. “Ad HoMiNeM aTtAcK ! ! !”
lol, nice backpedalling.
It’s you interpreting things out of thin air based on random marketing phrases on their homepage and posting a convo from Telegram where they had a difficult time understanding what you were saying (unsurprising, given your posts here) and eventually gave up responding since you were both condescending and hostile. Also once again using the word “guaranteed” out of the original context (the audit section), which they changed since it was indeed too much, even if it wasn’t saying what you claimed it was saying.
Same.
I just noticed this quote. You really like tooting your own horn. You 100% do not sound like “a high-ranking military officer or someone who works for an agency.” Honestly I think that you actually wrote that is kind of hilarious.
2 Likes